Post-quantum threats and current active interception techniques have forced a redesign of how multi-replica data strategies are verified in high-stakes industrial sectors. This critical shift is currently being led by a collaborative team of cryptographers from Huzhou Normal University and Zhejiang Gongshang University, whose latest research marks a defining moment in the evolution of cloud security. Published in the journal Mobile Networks and Applications, their work introduces the first publicly verifiable encryption scheme specifically engineered to withstand the most aggressive forms of cyber-interception, known as chosen-ciphertext attacks. By addressing the fundamental vulnerabilities in how global enterprises manage and verify encrypted backups across diverse cloud service providers, this breakthrough offers a resilient solution to the growing complexity of data sovereignty. As digital information becomes the primary asset of the modern economy, the ability to ensure that backup repositories remain untampered with—even when stored on third-party infrastructure—is no longer a luxury but a baseline requirement for institutional survival. This development comes at a time when traditional defenses are failing to keep pace with the sophisticated tools available to malicious actors, creating a need for a more robust mathematical foundation for cloud integrity.
The Mechanics: Public-Key Encryption with Equality Test
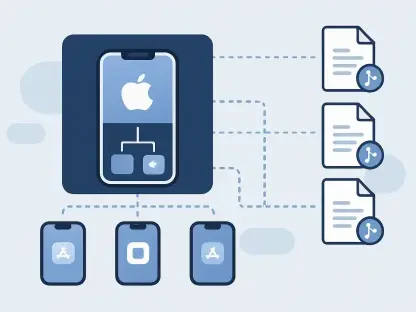
The foundation of this new security model is a specialized tool known as Public-Key Encryption with Equality Test, abbreviated as PKEET. This technology allows a cloud server to determine if two separate encrypted files contain the same original information without ever actually reading the sensitive data within. This capability is vital for large-scale data management, specifically for deduplication, where servers remove redundant copies to save space, and multi-replica strategies that ensure long-term reliability. Normally, standard encryption acts as a total blackout, making it impossible for a server to compare files without decrypting them first. However, PKEET provides a mathematical trapdoor that allows for comparison while maintaining absolute privacy for the user. By enabling this specific type of analysis, the system allows cloud providers to streamline their storage resources and verify that multiple backups across different geographic locations are identical. This process occurs without the provider ever having access to the decryption keys, thereby preserving the confidentiality of the stored records regardless of the physical location of the server.
For the past decade, PKEET models have evolved to support complex systems like the Industrial Internet of Things, yet they remained consistently vulnerable to active threats. The research team identified a critical flaw in previous versions that dominated the industry through 2024: they were only secure against chosen-plaintext attacks, where an adversary is assumed to be a passive observer of encrypted traffic. In the real world, hackers and sophisticated malicious entities are rarely passive. They often inject manipulated data or malformed ciphertexts into a system to observe how the server reacts, a method used to slowly leak information about the underlying plaintext. The new study highlights that even state-of-the-art models released in recent years failed to cross the chosen-ciphertext attack barrier, leaving them exposed to sophisticated manipulation by malicious insiders or external attackers. This vulnerability gap meant that while data was protected from prying eyes, the integrity of the verification process itself could be undermined by an attacker who understood how to trigger specific error responses from the cloud server.
Active Resistance: Bridging the Chosen-Ciphertext Attack Barrier
The new research bridges this historical security gap by focusing on resistance to active adversaries, specifically achieving the gold standard of chosen-ciphertext attack security. By ensuring that an attacker gains no useful information even when injecting garbage data or specifically crafted ciphertexts into the system, the researchers have created a defense suitable for high-stakes industries like finance and healthcare. In these sectors, simply guessing whether two encrypted files match can lead to a devastating privacy breach or a violation of strict regulatory requirements. This new construction ensures that the system remains airtight even under the pressure of a deliberate, calculated attack intended to exploit the equality test function. The mathematical framework is designed to detect and reject malformed inputs before they can leak any relational data, effectively neutralizing the primary weapon of modern interceptors. This move from passive to active defense represents a necessary evolution in cloud storage, where the assumption of a benign or merely curious observer is no longer a realistic basis for a security architecture in a hostile digital landscape.
In addition to active defense, the scheme introduces a decentralized approach to verification that fundamentally changes the trust relationship between clients and providers. Rather than forcing a client to trust a single cloud provider to accurately report the status of their data, the task of checking data equality is shared across multiple authorized servers. The system generates a compact cryptographic proof of correctness that allows any third party—such as a government regulator, an independent auditor, or an insurance company—to verify that the data is correct. This verification requires no secret keys and never exposes the underlying information to the auditor. It effectively shifts the cloud storage paradigm from a model based on blind trust in a corporate entity to one based on verifiable mathematical evidence. This transparency is achieved through a public auditing feature that allows for continuous monitoring of data integrity without interrupting the primary operations of the storage provider. It allows organizations to prove compliance with data retention policies while maintaining a zero-trust posture regarding the actual storage hardware.
Operational Efficiency: Balancing Security and Performance
The reliability of this encryption breakthrough is rooted in well-established mathematical principles, specifically bilinear pairings and the complexity of Diffie-Hellman problems. The researchers used rigorous modeling to prove three distinct levels of security: protection against internal threats, protection against external hackers, and the inability to fake results. These proofs ensure that a cloud server cannot snoop on data and that it is mathematically impossible for an attacker to produce a fake proof claiming two files match when they actually do not. This property, known as unforgeability, is the cornerstone of the system’s reliability, as it prevents malicious providers from lying about the existence or status of a backup. The mathematical rigor of the scheme ensures that even if an attacker manages to compromise one part of the infrastructure, the overall integrity of the data verification remains intact. This layered approach to security provides a much-needed safety net for organizations that have increasingly decentralized their data across various global jurisdictions, where legal protections for data may vary significantly but mathematical laws remain constant.
A common concern in the field of cryptography is that increased security usually results in significantly slower system performance. However, this study defies that trend by demonstrating remarkable efficiency in its implementation. When compared to the leading models from 2024, the new chosen-ciphertext attack secure scheme actually reduced the computational cost of public verification by 24 percent. By making the process both cheaper to run and more secure, the researchers have turned a complex theoretical concept into a practical tool that can be deployed in massive data centers where millions of files require constant integrity checks. This efficiency gain is particularly important for high-velocity data environments where the time taken to verify a backup can impact the overall availability of the system. The ability to perform high-level security checks without a significant performance penalty makes it feasible for organizations to implement this technology across their entire data footprint, rather than just for their most sensitive files. This ensures a uniform standard of protection that is both sustainable and scalable as data volumes continue to grow exponentially.
Strategic Implementation: The Future of Industrial Data Management
The practical implications of this breakthrough are far-reaching, particularly for sectors with strict regulatory requirements and high data sensitivity. In the world of e-health, hospitals can store patient records across various cloud platforms while allowing regulators to confirm the consistency of those records without ever violating patient privacy. Similarly, financial institutions can prove to auditors that their global archives are intact and correctly duplicated across redundant servers, satisfying right to audit clauses while maintaining top-tier encryption standards. This creates a trustless architecture where security is guaranteed by the cryptographic code itself rather than the promises of the service provider. For the manufacturing sector, which relies heavily on the Industrial Internet of Things, this scheme ensures that device configurations and operational logs remain consistent across the supply chain, preventing unauthorized modifications that could lead to physical safety risks. By integrating these verifiable proofs into standard operating procedures, companies can automate their compliance workflows and reduce the risk of human error during complex auditing processes.
In the long term, the migration from passive to active security models was recognized as an essential step for the survival of secure cloud storage. As more sensitive intellectual property migrated to the cloud, the assumption that an attacker would remain passive became a dangerous and costly gamble. Although the study acknowledged certain technical limitations, such as the need for eventual post-quantum adaptations to defend against future computing threats, it effectively eliminated the traditional trade-off between the ability to manage data and the ability to keep it secure. Organizations were advised to begin evaluating their current backup architectures to identify where publicly verifiable equality tests could be integrated to replace outdated trust-based systems. Implementing these advanced cryptographic primitives allowed for a more granular control over data visibility while streamlining the deduplication processes that keep storage costs manageable. By adopting these verified standards, the industry moved toward a more transparent and resilient digital future where data integrity is maintained through rigorous mathematical proofs rather than simple perimeter defenses.