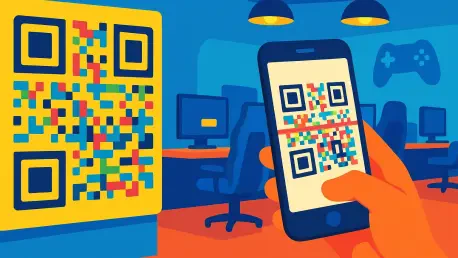
Security researchers discovered that the Mario Kart Live: Home Circuit QR code scanning process provides a specific entry point for exploiting vulnerabilities in the console’s local wireless networking. Imagine a scenario where a simple peer-to-peer image transfer at a local gaming tournament becomes the unintended gateway for a sophisticated memory-corruption attack. This flaw, officially tracked as CVE-2026-82079, exposes a significant security vulnerability within the firmware of the original Nintendo Switch hardware. The core of the issue is a stack-based buffer overflow, which occurs when the system’s memory is overwhelmed by incoming data that exceeds its pre-allocated capacity. By sending specially crafted network traffic, an attacker can corrupt the device’s memory to execute unauthorized code via return-oriented programming. This technique allows for the manipulation of the console’s internal processes by chaining together existing instruction sequences that the operating system would normally consider safe.
1. Technical Analysis of Localized Wireless Exploitation
The exploitation process for CVE-2026-82079 is intrinsically linked to the way the console handles temporary local networking environments during high-interaction gaming sessions. When a user engages in activities like sharing screenshots or playing augmented reality titles, the device establishes a localized wireless connection to facilitate rapid data exchange with external hardware. An attacker must be within the immediate wireless range and must directly interact with a QR code displayed on the console’s screen or a connected television. This interaction allows the malicious device to join the private network and begin transmitting the crafted packets necessary to trigger the buffer overflow. Because the system does not sufficiently validate the size of the incoming data packets during this handshake, it becomes vulnerable to memory corruption. This breach of system integrity allows for the execution of arbitrary operations that would otherwise be restricted by the layers of the operating system.
Specific workflows within the Nintendo ecosystem are more susceptible to this type of attack than others, particularly those that rely on the console’s native capability to send data to smartphones. This feature, found within the system’s Album application and utilized by titles like Mario Kart Live: Home Circuit, creates a bridge between the console and a mobile device via a QR code scan. During this window of connectivity, the console’s networking code is briefly exposed to external inputs, which an adversary can manipulate if they are physically present. The requirement for direct visual access to the QR code and close proximity to the hardware acts as a significant barrier to large-scale or remote exploitation. Nevertheless, the risk remains pertinent in public or semi-public gaming spaces where multiple users might be interacting with wireless features simultaneously. The vulnerability demonstrates that even convenience-focused features can introduce complex security challenges if the memory management is not robust.
2. Assessment of Risk and Remediation Strategies
The severity of this flaw is categorized as high, with a CVSS 4.0 base score of 7.0, reflecting its potential to compromise the confidentiality and integrity of the system. While the attack complexity is low and requires no special privileges, the necessity of adjacent-network access and passive user interaction limits the overall threat profile. Interestingly, the newer Nintendo Switch 2 hardware is completely unaffected by this specific vulnerability, as the manufacturer implemented different networking protocols and memory handling in the updated architecture. For users of the original hardware, the primary defense is the installation of system update 23.0.0, which was released to specifically address and patch the buffer overflow. Despite the technical potency of the exploit, current predictive models suggest a very low probability of this vulnerability being successfully utilized in widespread real-world attacks. This indicates that the logistics of execution prevent it from becoming a common threat for most gamers.
Building upon these technical concerns, the most critical step involved the immediate transition to the 23.0.0 firmware, which effectively closed the networking entry point. For those who could not update their consoles right away, maintaining a high level of situational awareness regarding their physical surroundings provided a necessary layer of protection. Owners were encouraged to avoid using the Album sharing functions in unfamiliar locations and to prevent strangers from scanning any QR codes generated by their systems. Additionally, users relied only on trusted personal smartphones for local transfers and were cautious when using augmented reality peripherals in crowded environments. These proactive measures successfully mitigated the risks associated with the high-severity vulnerability during the initial disclosure period. By following these established security protocols, the gaming community demonstrated a strong commitment to hardware integrity. This experience highlighted the importance of regular updates and vigilance.